云原生
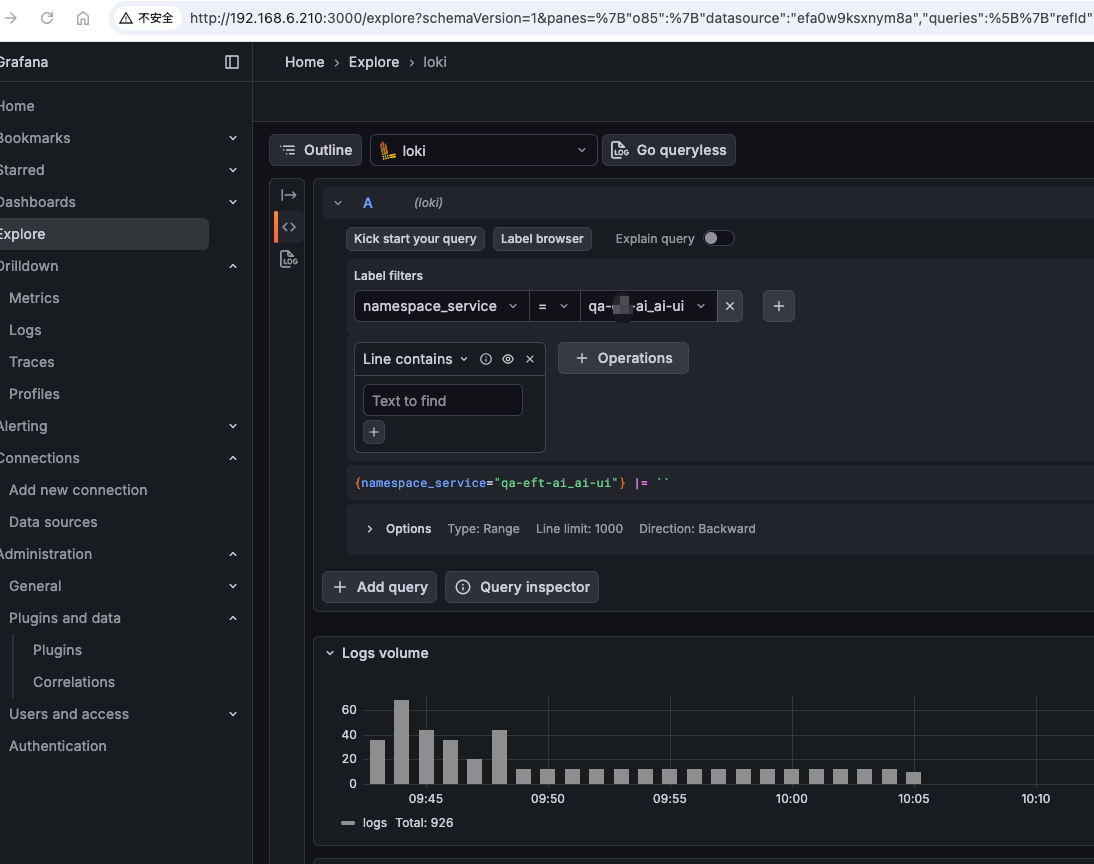
利用kurise做日志采集使用promtail做sidecar采集日志
利用OpenKurise中的kruise做日志采集,原来我使用的是filebeat作为sidecar采集日志的,虽然采集没有什么问题,但是通过es进才看日志就比较繁琐了,这次实验p
RBAC(Role-Based Access Control)是 Kubernetes 中最核心、最常用的权限控制模型。无论你是平台管理员、SRE,还是 K8s 应用开发者,只要你需要安全地管理集群访问,RBAC 都是绕不过去的。
本篇文章将用“易懂 + 专业 + 示例驱动”的方式,从底层概念到实战案例帮你完全吃透 RBAC。
RBAC = 根据角色分配权限。在 Kubernetes 中,它控制:
用户能做什么(verbs)
能操作哪些资源(pods、deployments…)
作用范围(namespace / cluster)
Kubernetes 不会直接给用户权限,而是让用户绑定角色,角色里定义了权限。
RBAC 可以解决如下问题:
开发人员误删 Pod
CI/CD 仅读 Pod 却无法创建 Deployment
用户报 Forbidden 403
多 namespace 场景的权限隔离
RBAC 一共有 4 种对象:
| 对象 | 作用范围 | 作用 |
|---|---|---|
| Role | namespace | 定义某个命名空间内的权限 |
| ClusterRole | 全局 | 定义集群级别权限 |
| RoleBinding | namespace | 绑定 Role 或 ClusterRole 给用户 |
| ClusterRoleBinding | 全局 | 将 ClusterRole 绑定给用户(全局生效) |
关键词:
Role = 权限列表
Binding = 用户与角色的关系
ClusterRole = 跨命名空间或全局资源
权限由以下三部分组成:
apiGroups
resources
verbs
 apiVersion: rbac.authorization.k8s.io/v1
 kind: Role
 metadata:
   name: pod-reader
   namespace: dev
 rules:
   - apiGroups: [""]
     resources: ["pods"]
     verbs: ["get", "list", "watch"]
 apiVersion: rbac.authorization.k8s.io/v1
 kind: ClusterRole
 metadata:
   name: node-reader
 rules:
   - apiGroups: [""]
     resources: ["nodes"]
     verbs: ["get", "list"]
 apiVersion: rbac.authorization.k8s.io/v1
 kind: RoleBinding
 metadata:
   name: bind-pod-reader
   namespace: dev
 subjects:
   - kind: User
     name: alice
     apiGroup: rbac.authorization.k8s.io
 roleRef:
   kind: Role
   name: pod-reader
   apiGroup: rbac.authorization.k8s.io
 apiVersion: rbac.authorization.k8s.io/v1
 kind: ClusterRoleBinding
 metadata:
   name: bind-read-all
 subjects:
   - kind: User
     name: bob
     apiGroup: rbac.authorization.k8s.io
 roleRef:
   kind: ClusterRole
   name: cluster-admin
   apiGroup: rbac.authorization.k8s.io
| 动作 | 含义 |
|---|---|
| get | 读取 |
| list | 列表 |
| watch | 监听 |
| create | 创建 |
| update | 更新 |
| patch | 局部更新 |
| delete | 删除 |
| exec | 执行容器命令 |
| use | 使用特定权限(如 PSP) |
| 资源 | APIGroup |
|---|---|
| pods | "" |
| deployments | apps |
| services | "" |
| nodes | "" |
| configmaps | "" |
| secrets | "" |
| ingress | networking.k8s.io |
| crd | apiextensions.k8s.io |
 rules:
   - apiGroups: [""]
     resources: ["pods"]
     verbs: ["get", "list", "watch"]
verbs: ["get", "list", "watch", "create", "update", "patch"]
 resources: ["nodes"]
 verbs: ["get", "list"]
 resources: ["pods/exec"]
 verbs: ["create"]
 resources: ["pods/log"]
 verbs: ["get", "list"]
 apiGroups: ["apiextensions.k8s.io"]
 resources: ["customresourcedefinitions"]
 verbs: ["*"]
 apiVersion: v1
 kind: ServiceAccount
 metadata:
   name: app-sa
   namespace: dev
 kind: RoleBinding
 subjects:
   - kind: ServiceAccount
     name: app-sa
     namespace: dev
 roleRef:
   kind: Role
   name: pod-read
 spec:
   serviceAccountName: app-sa
kubectl auth can-i create pods --as alice -n dev
输出 yes → 有权限
输出 no → 没权限
遵循最小权限原则
开发人员按 namespace 授权,不给全局权限
系统组件统一使用 ServiceAccount
高危权限拆分 Role
建立公司级标准 Role 库
避免直接给人类用户 cluster-admin
RBAC 核心就是:
 User / ServiceAccount
         ↓
 Binding (RoleBinding / ClusterRoleBinding)
         ↓
 Role / ClusterRole
         ↓
 Resources + Verbs
利用OpenKurise中的kruise做日志采集,原来我使用的是filebeat作为sidecar采集日志的,虽然采集没有什么问题,但是通过es进才看日志就比较繁琐了,这次实验p

在 Kubernetes 环境下,通过 Filebeat 采集容器日志并将其转发至日志平台(如 Kafka、Elasticsearch)是一种常见的日志解决方案。为了实现日志的可观

在kubernetes中1.28以前的版本如果想升级几年不太支持,但是每次要手动进行续签又太麻烦,所以我想做一个定时续签的功能,这样保证每次到期的时候不需要认为的去操作, 我这里的
评论 0